The page checks before it asks
An unknown audience or a disallowed return address gets a dead end, not a form. Credentials are never collected for a destination the server has not vouched for.
The front door
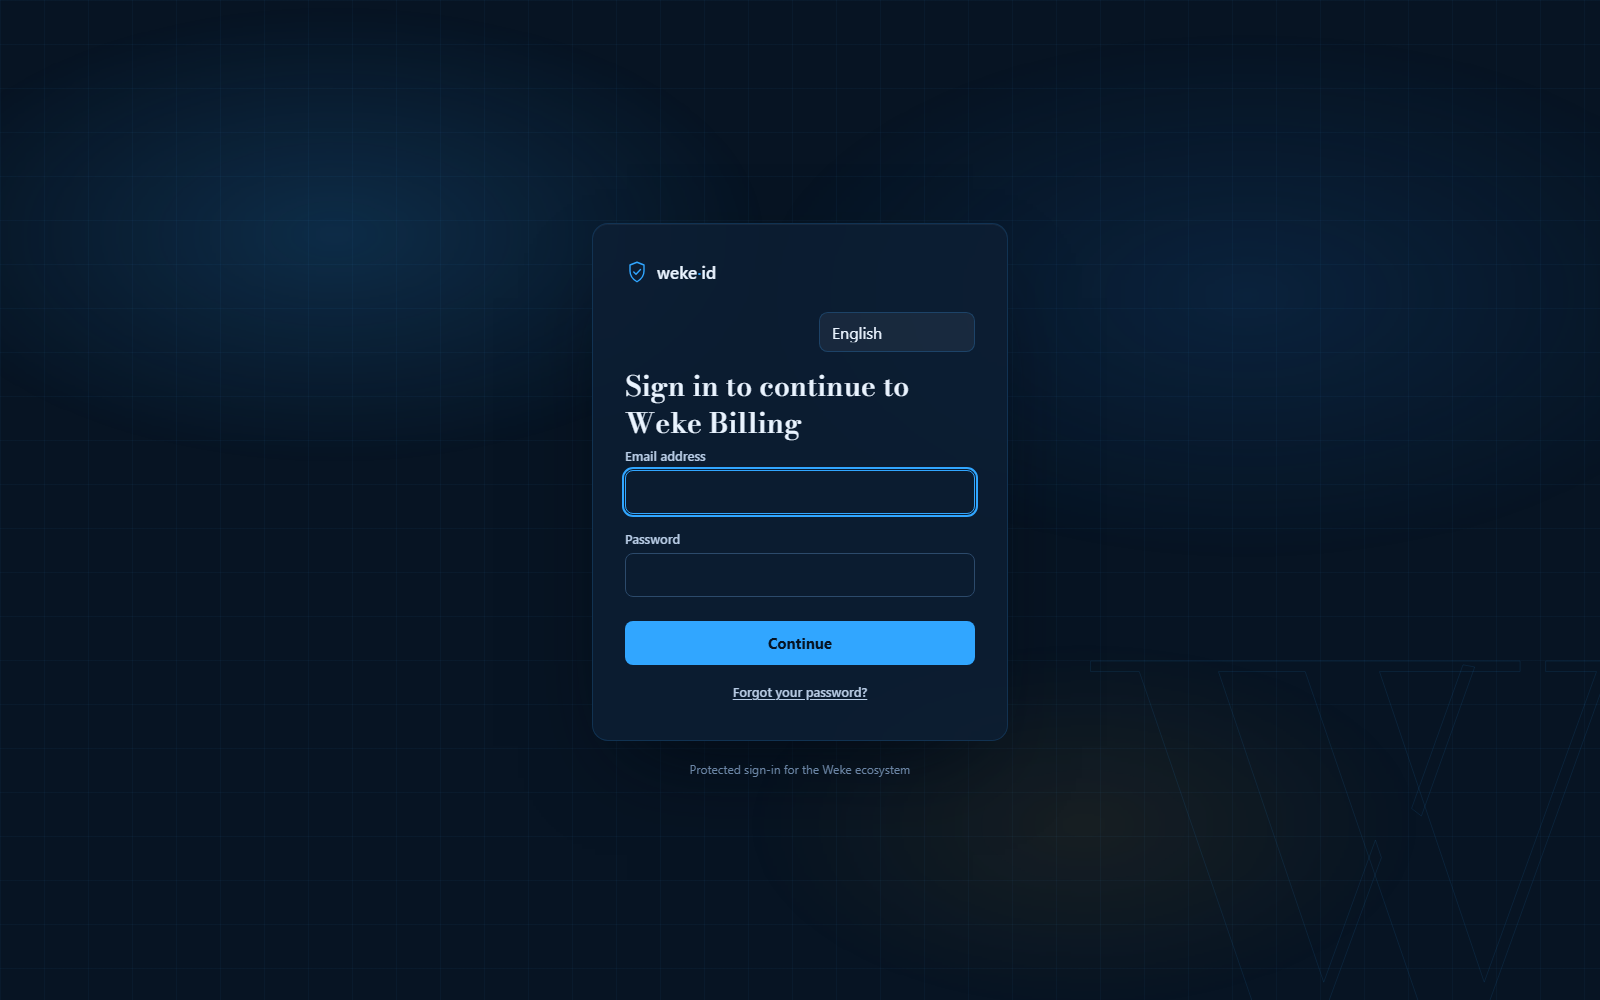
Every console launches the same hosted sign-in. Before a single field renders, the page asks the server whether the app and return address are legitimate — and if they are not, no form ever appears.
An unknown audience or a disallowed return address gets a dead end, not a form. Credentials are never collected for a destination the server has not vouched for.
Accounts with two-step verification get the TOTP challenge in the same card — with backup codes for the day the phone is gone.
The sign-in page runs under its own strict CSP — no inline code, no third-party hosts, no framing — with a rate limiter watching the one endpoint that does real work.
At the door
The hosted sign-in in the platform's research-editorial language — serif heading, aurora, blueprint grid, and the name of the console you are entering.